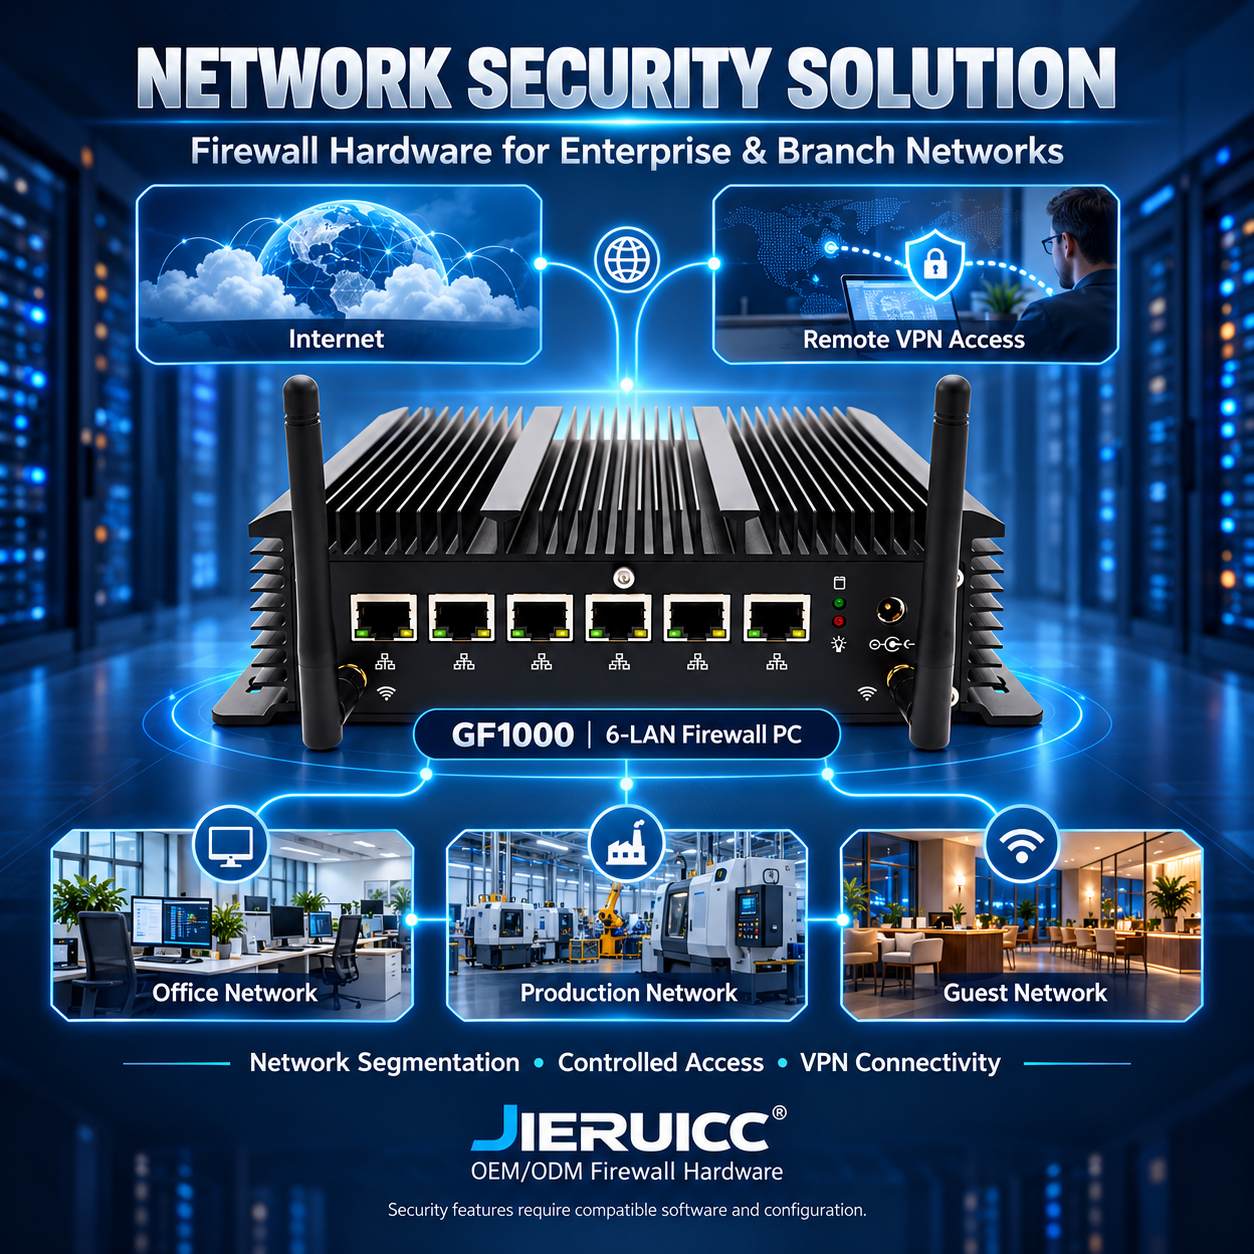
Enterprise offices, chain stores, and factory networks often face similar problems: guest devices and business systems sharing the network, lack of access control for remote maintenance, difficulty in uniformly deploying branch office equipment, and insufficient performance after enabling security features.
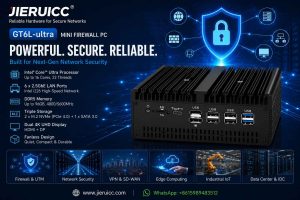
JIERUICC is an OEM/ODM hardware manufacturer of Mini PCs and Firewall PCs, providing multi-port firewall hardware for network security solution providers, system integrators, resellers, and enterprise procurement. Paired with compatibility-proven firewall software, it can be used for network isolation, VPN access, access control, and log management.
**1. Enterprises and Branch Offices: Isolating Business Networks and Reducing Unauthorized Access**
Sharing a network between office computers, POS systems, cameras, and guest Wi-Fi increases the risk of unauthorized access between devices.
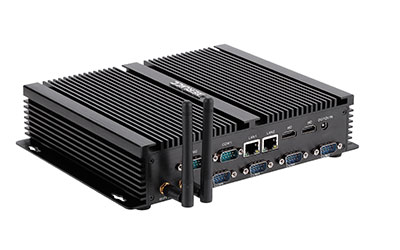
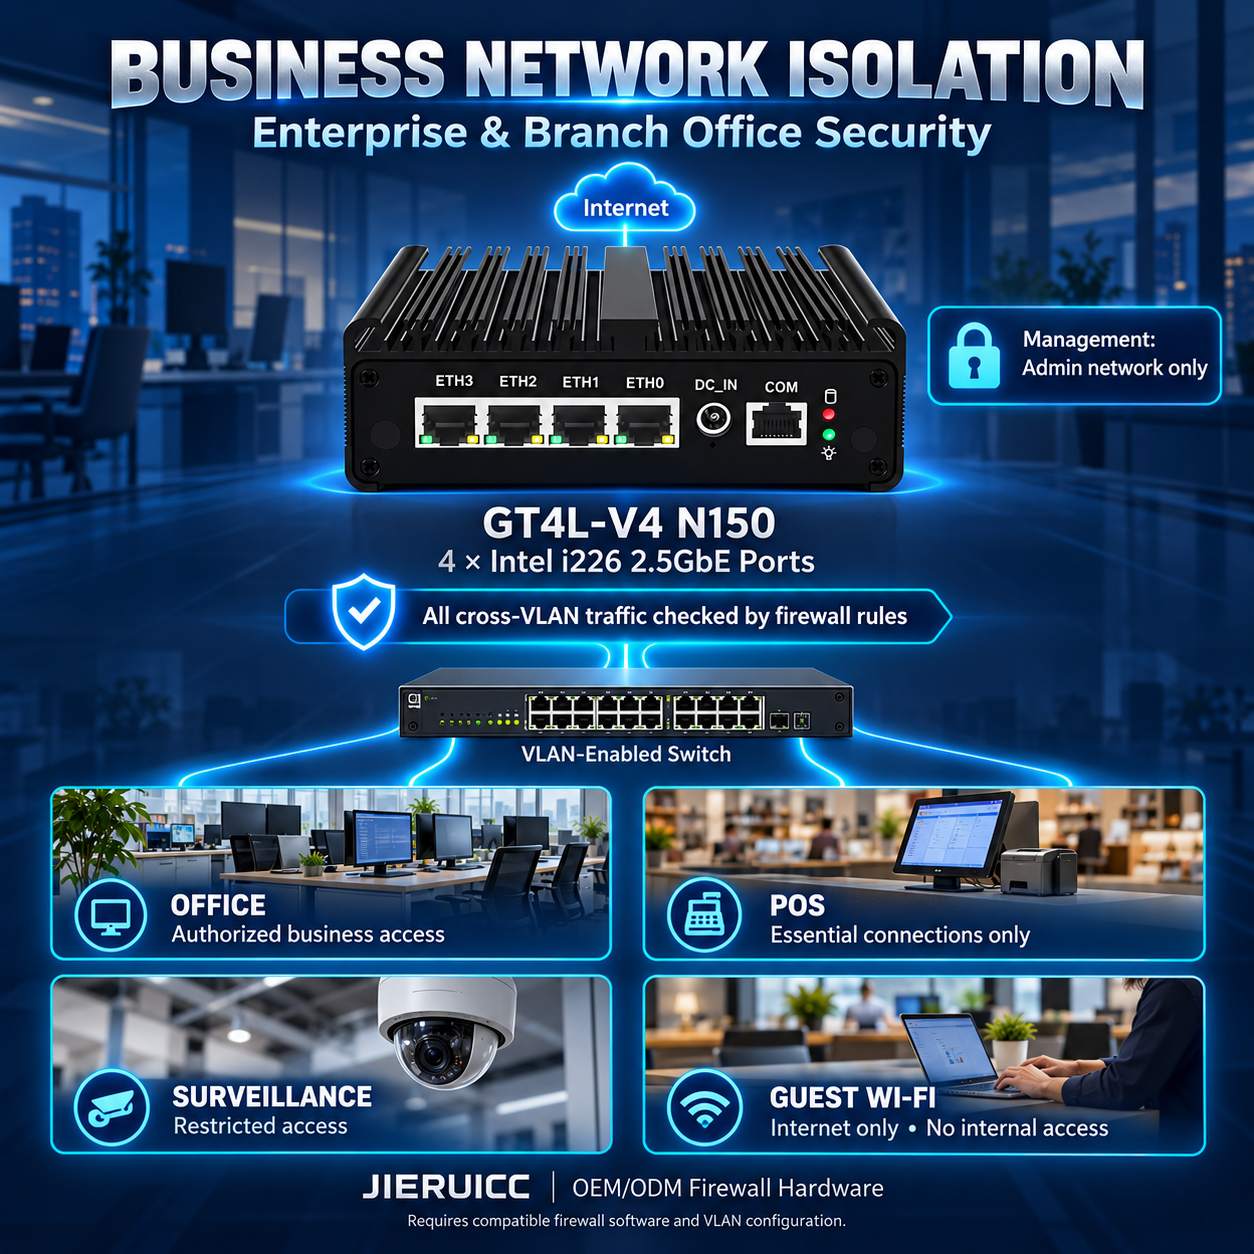
The **GT4L-V4 N150 Firewall Host** can be used, utilizing four Intel i226 2.5GbE ports to connect the internet to different business networks. Combine VLAN-enabled switches to divide office, POS, monitoring, and visitor devices into independent network segments.
During deployment, prohibit visitor network access to internal business systems; allow the POS network only the necessary business connections; and restrict device management access to the administrator network segment. Cross-segment traffic must be inspected by firewall policies.
**2. Factory and Branch Offices: Divide Security Zones and Control Remote Maintenance Access**
Production equipment, office systems, and external maintenance personnel require different access permissions.
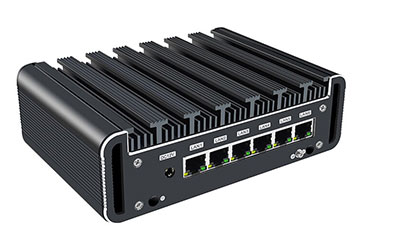
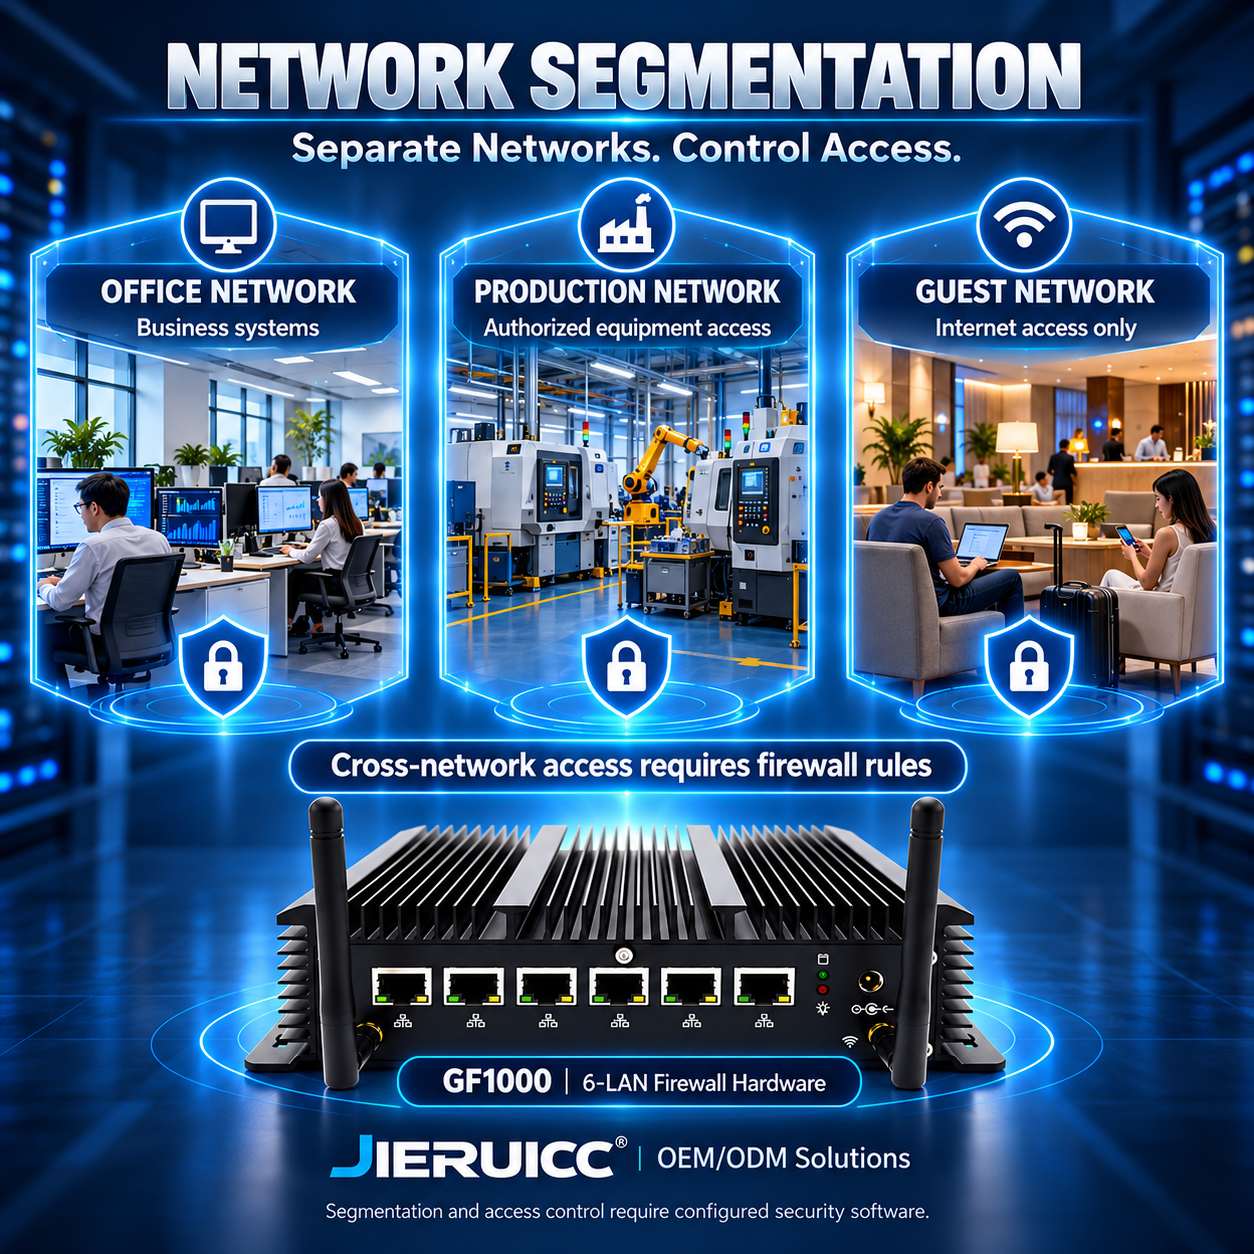
**The GF1000 six-port fanless firewall host** can be used to connect WAN, office network, production network, device network, and management network. Its fanless aluminum alloy chassis is suitable for deployment environments with requirements on noise and fan maintenance. Processor, memory, and storage can be configured according to the project.
It is recommended to prohibit unnecessary access between security zones by default, allowing only business communication based on device IP, port, and business protocol. Remote maintenance is accessed via VPN, and with the help of multi-factor authentication, time-limited accounts, and access logs supported by the selected software, device management ports should not be directly exposed to the Internet.
Before factory deployment, verify the operating temperature, power supply, and installation conditions, and confirm production communication at the maintenance window.
**3. High-Speed Network: Matching Fiber Optic Uplink and Security Requirements**
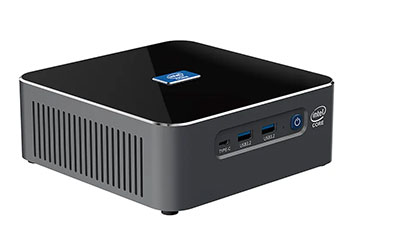
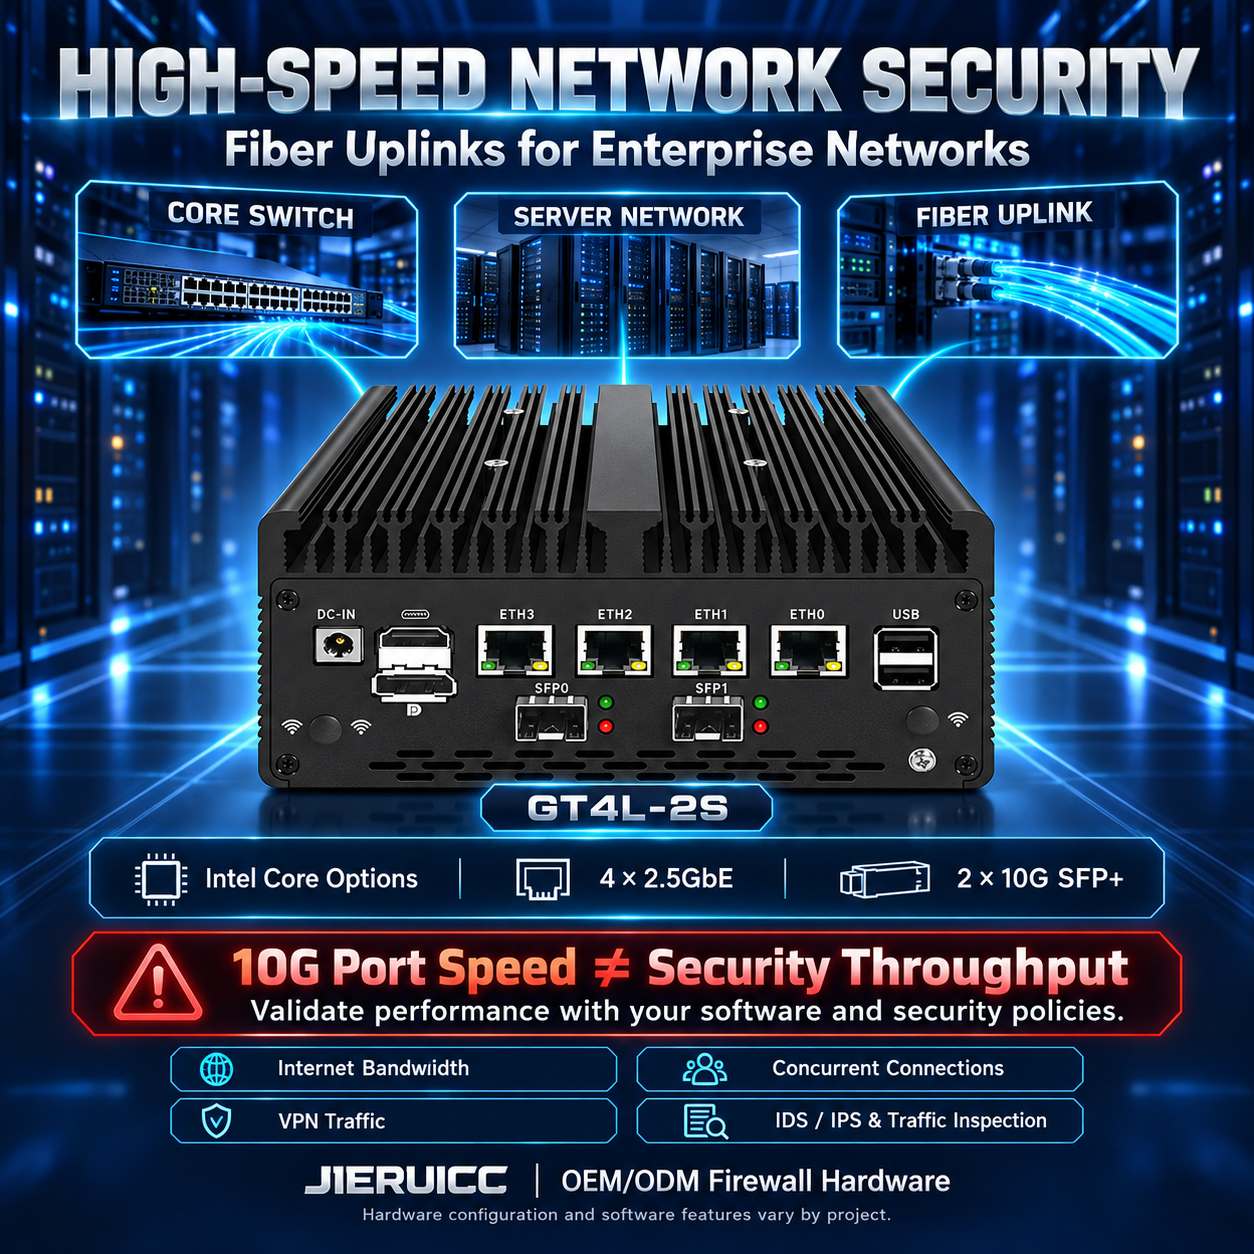
For projects requiring connections to core switches, server areas, or high-speed uplinks, evaluate the **GT4L-2S / GT4L-4S series**, selecting an Intel Core processor, four 2.5GbE Ethernet ports, and a 10G SFP+ expansion interface according to the configuration.
Selection should consider internet bandwidth, concurrent connections, VPN traffic, and whether intrusion detection, prevention, or deep traffic inspection is enabled. **10G interface speed does not equal actual throughput after enabling security features**; the final configuration should be based on test results under the target software and actual policies.
**4. Feasible Deployment Process**
- **Define Requirements:** Provide network topology, bandwidth, number of terminals, VPN concurrency, required security features, and installation environment.
- **Hardware and Software Confirmation:** Identify the CPU, network card, memory, and SSD; verify the target software version, drivers, and required functionality.
- **Security Policy Configuration:** Divide the network into zones, adopt the least privilege rule, disable public network management access, and configure VPN, logging, and alarms.
- **Prototype Acceptance:** Test allowed and prohibited access, VPN stability, and throughput, latency, and sustained performance after enabling actual security policies.
- **Standardized Delivery:** Solidify hardware configurations and software versions, and maintain configuration backups; use independent credentials for each device, and establish update and fault recovery procedures.
**5. OEM/ODM Support for Bulk Projects:**
JIERUICC can provide customization for processors, memory, storage, and brand appearance based on project requirements. Interface and structural adjustments are evaluated by the engineering team. Bulk production begins only after configuration confirmation via prototype, helping partners reduce redundant selection and deployment work.
JIERUICC provides the hardware platform and related hardware technical support; firewall, VPN, intrusion prevention, and centralized management functions are implemented by the selected software and its configuration. Software licensing and maintenance scope are defined during project confirmation.
**Obtain the Firewall Hardware Configuration Suitable for Your Project**
Please provide the target software, network bandwidth, number and speed of network ports, VPN requirements, installation environment, and purchase quantity. JIERUICC will assist in matching hardware configurations, supporting everything from prototype verification to mass production delivery.